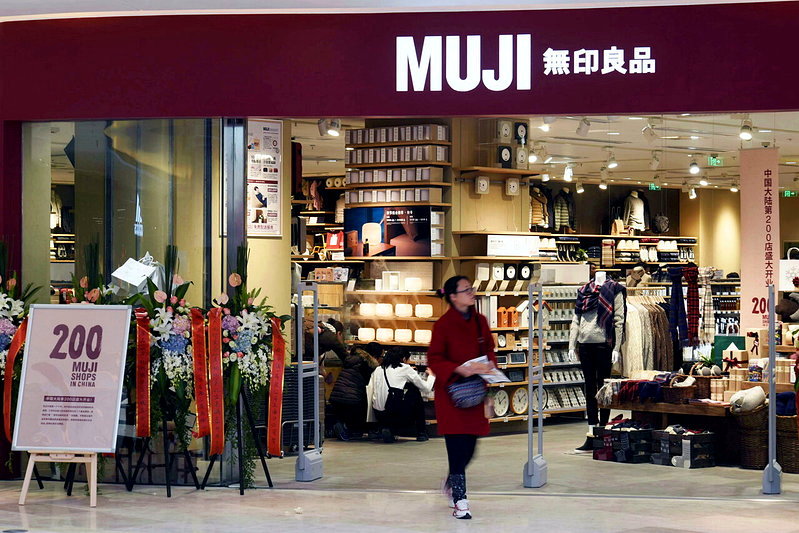

Japan Ryohin KKK Co., Ltd., the operator of daily grocery brand MUJI, said today that its official application “MUG APP” suffered unauthorized access and information of 27.26 million customers may have been leaked, but the names and credit card information were not leaked.
Ryohin Keikai Co., Ltd. reported that the information that may have been leaked includes email address, date of birth, and gender, as well as information about customers who have stopped using the MUJI app.
Although there is no confirmation that the leaked data has been misused, Ryohin Keikan has urged customers not to click on links in suspicious emails to avoid falling for phishing scams. The company will notify affected customers individually.
Ryohin Co., Ltd. said that the MUJI APP and online store will continue to operate normally.