
AI summary
Summary of article:
The refrigeration systems of many supermarkets and blood centers in France have been attacked by a series of cyber attacks, exposing the risks of connected equipment. The government has therefore expedited the review of the Information Security Bill, hoping to strengthen the security of critical facilities through standards such as NIS 2.
Refrigeration equipment and blood center refrigeration systems in several French supermarkets have recently been attacked by cyber attacks, highlighting the public safety risks and economic losses caused by cyber attacks. Faced with a serious situation, France is accelerating legislation to strengthen the cybersecurity resilience of critical facilities.
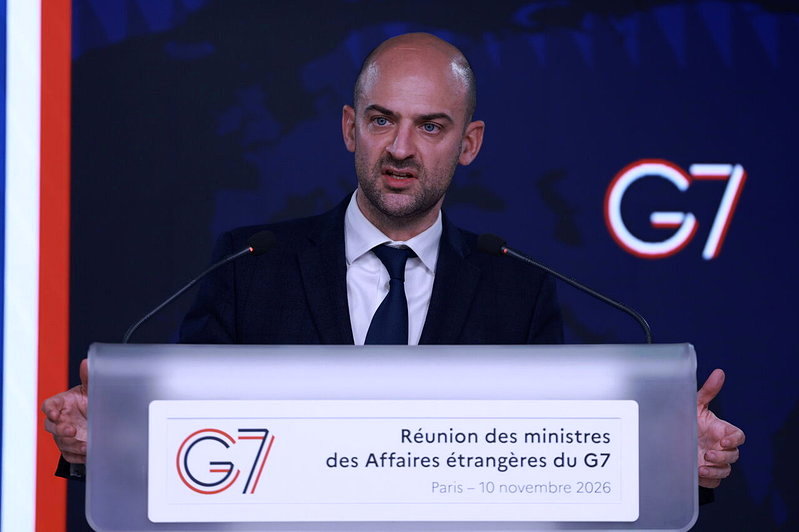
In mid-October this year, the control systems of refrigeration or freezing equipment of hundreds of large retailers such as Carrefour and Monoprix in France suffered cyber attacks, causing the equipment’s temperature to rise and causing operators to abandon a large number of goods. French Foreign Minister Jean-Noel Barrot recently allegediran He is the mastermind behind this wave of attacks, but Iran denies this.
Additionally, the cold storage of a French blood center, which stored blood samples and plasma bags used for blood transfusions and pharmaceuticals, was also attacked earlier this month, but there was no impact or loss. Paris prosecutors are investigating the case.
The French Senate passed a bill aimed at strengthening the digital security of infrastructure in 2025. Due to frequent incidents of various cyber attacks, the bill was finally included in the agenda of the National Assembly earlier this week and the consideration resumed.
this bill will beEuropean Union Three directives were transposed into French law, including NIS 2, passed by the EU in 2022. It was originally scheduled to take effect in France in October 2024, but the French Senate only passed the bill in March 2025, and then it must be passed by the National Assembly.
NIS 2 stipulates that critical or critical entities must implement a set of minimum rules, such as regularly updating systems, increasing staff vigilance against phishing, and creating security policies.
Cybersecurity expert Rena Stambolińska told Liberation that from a technical point of view, these rules are not new, but rather are basic norms aimed at protecting the security of authority and personnel, implementing monitoring, detecting and responding to anomalies, but they are still far from being universally applied.
Facing a growing serious threat, the Bill significantly expands the scope of entities subject to control, covering public administration departments, postal services, waste management, food sectors, etc., and will punish entities violating the rules, including higher fines, and even senior corporate executives can be held personally liable.
The French National Agency for the Security of Information Systems (ANSSI) mentions in its Industrial Systems Cybersecurity Guidelines some dangerous practices that can put connected devices at risk. For example, many people are accustomed to “not changing any settings as long as the system is operating normally” or “contracts prohibit modifications to the existing system, including the implementation of network security measures.”
France News (FranceInfo) reported that nowadays more and more devices in every home and enterprise are connected to the Internet. The advantage is that they can be controlled remotely, reducing the cost of actual on-site control. These can also be operated in groups and transmit data which is beneficial for monitoring.
However, currently, users rarely prioritize the security of these systems, perhaps because they are unaware that hackers are interested in connected devices such as refrigerators. Thomas Guyette, general manager of cybersecurity company Discovery, warned: “When items are connected to the Internet, it is equivalent to bringing security risks into the physical world.”
Summary FAQ
-
The refrigeration and freezing control systems of supermarkets such as Carrefour and Monoprix were attacked, causing temperatures to rise and products to be destroyed. The cold storage of the blood center was also attacked, but no real damage was caused.
-
Incidents like the one at the supermarket and the blood bank have shown that cyberattacks are not just data risks, but can also impact supply chains and public safety. The government is expected to pass legislation to improve the resilience of critical facilities in the face of attacks.
-
The bill would incorporate EU directives such as NIS 2 into domestic law, require system updates, strengthen employee vigilance and security policies and expand controls to more areas. Violators may face high fines and personal responsibility of the supervisor.