
AI summary
Summary of article:
Hackers spread malicious programs under the guise of job interviews to trick engineers into downloading and executing projects through a backdoor. Microsoft and Atlassian remind job seekers to test in an isolated environment to avoid theft of credentials and corporate systems.
Even a seemingly simple interview can become a medium for hackers to attack your computer.Southern California An engineer named Liu said a recruiter recently contacted him through LinkedIn and asked to review a coding project, only to discover that it contained a suspicious backdoor.Microsoft And software company Atlassian has disclosed similar tactics, and even security company Sophos employees have fallen victim to it.
Mr. Liu said that after the abnormality was discovered, he immediately checked whether the development environment was affected. He lamented that “people’s hearts are really bad” and reminded job seekers to raise awareness of security issues. However, the post does not explain the entire technical analysis and subsequent inspection results, and it is not yet possible to confirm whether the data has been leaked or not. Some netizens also shared that they were repeatedly asked by recruiters whether the project was executed, and they suspected that the recruiters were confirming whether malicious programs were activated.
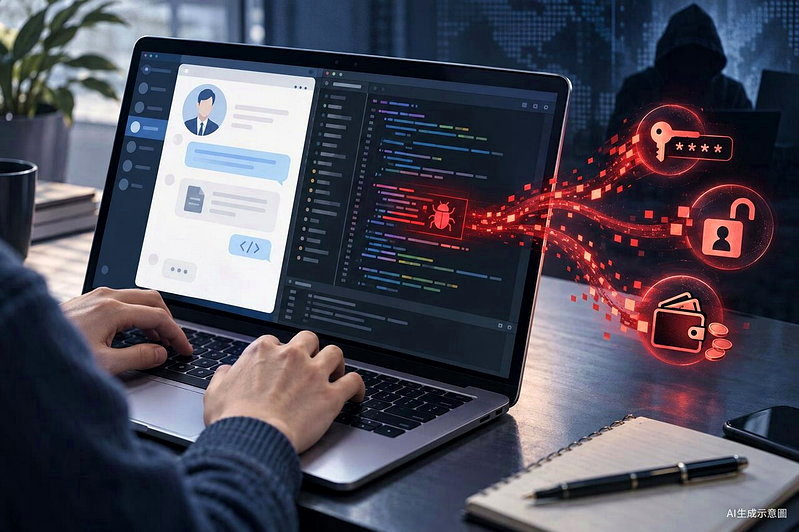
There have been actual cases of infiltration of this type of web. The Sophos investigation report said an employee downloaded an “interview assignment” onto a company-issued Mac computer on September 14 and opened it with the development tool Visual Studio Code (VS Code). The project included a modified configuration file. When employees opened the built-in terminal, the computer began downloading and executing malicious programs.
The Sophos investigation also found that third-party application authorization linked to the employee’s account was exploited to issue unauthorized read requests to two internal code libraries, but no access to the company’s products, services or customer data was found. Although the employee’s computer had protective software installed, it was not functioning properly at the time.
Microsoft also released research in March this year showing that in an attack called “infectious interviewing”, hackers pretended to be recruiters from cryptocurrency trading companies and artificial intelligence companies, tricking engineers into downloading and executing projects. Some projects use VS Code’s Automated Tasks function to execute hidden instructions and download backdoor programs after the user clicks to trust the project.
Atlassian research in September concluded with a high level of confidence that the attack was related to North Korean hackers. The report notes that these projects may appear to be complete applications, but may contain only a few lines of malicious code among thousands of lines of code. Once executed, they can steal account credentials, API keys, and cryptocurrency wallet information, and even gain access to enterprise systems. The attackers also asked applicants to record the process of explaining “interview assignments” and upload a copy of the project to GitHub or Bitbucket, so that applicants could unknowingly help spread the malicious program.
Microsoft and Atlassian suggest that job seekers should use separate virtual machines and other testing environments to complete interviews and avoid executing unfamiliar projects on work computers that have access to company systems and critical credentials. Atlassian also reminded that VS Code’s automatic task execution function should be turned off; If it is suspected that the device has been attacked, the network should be immediately disconnected, the password from the security device should be changed, login authorization should be revoked, and the corresponding keys should be replaced.
Summary FAQ
-
The hacker first pretends to be a recruiter to contact the job seeker on LinkedIn, and then requests to download and execute the project under the pretext of reviewing or completing an interview assignment; Once the user opens it in development tools, the hidden command can be triggered.
-
The employee downloaded the “Interview Assignment” onto a company-issued Mac and opened it with VS Code. When the modified configuration file in the project was started on a terminal, it began downloading and executing malicious programs, further attempting to access internal resources.
-
Microsoft and Atlassian recommend using a separate virtual machine or testing environment to handle interview assignments, not executing unfamiliar projects on a work computer with access to company credentials, and turning off VS Code’s automatic task execution feature.